▸ Category · Laravel
Notes on Laravel.
8 posts in this category.
-
 Laravel
MCP auth and audit logging in a Laravel SaaS
An MCP server on Laravel is only as safe as its tenancy boundary. Scoped tool auth, request-bound actor context, and an audit log you can actually read at 3am.
Read post →
-
 Laravel
MCP OAuth PKCE for multi-tenant SaaS
Laravel MCP requires PKCE S256 and prefers Client ID Metadata Documents. How multi-tenant SaaS should bind workspace at consent and avoid common agent auth failures.
Read post →
-
 Laravel
Stateless MCP servers on Laravel
Laravel MCP 1.0 drops session IDs. Scale with Octane and queues, keep auth and idempotency, and pass your own correlation ids in _meta.
Read post →
-
 Laravel
 MCP searchable tool catalogs
Laravel MCP 1.0 searchable catalogs and cache hints cut context bloat. When to expose tools versus discover them with search_tools and execute_tools.
Read post →
-
 Laravel
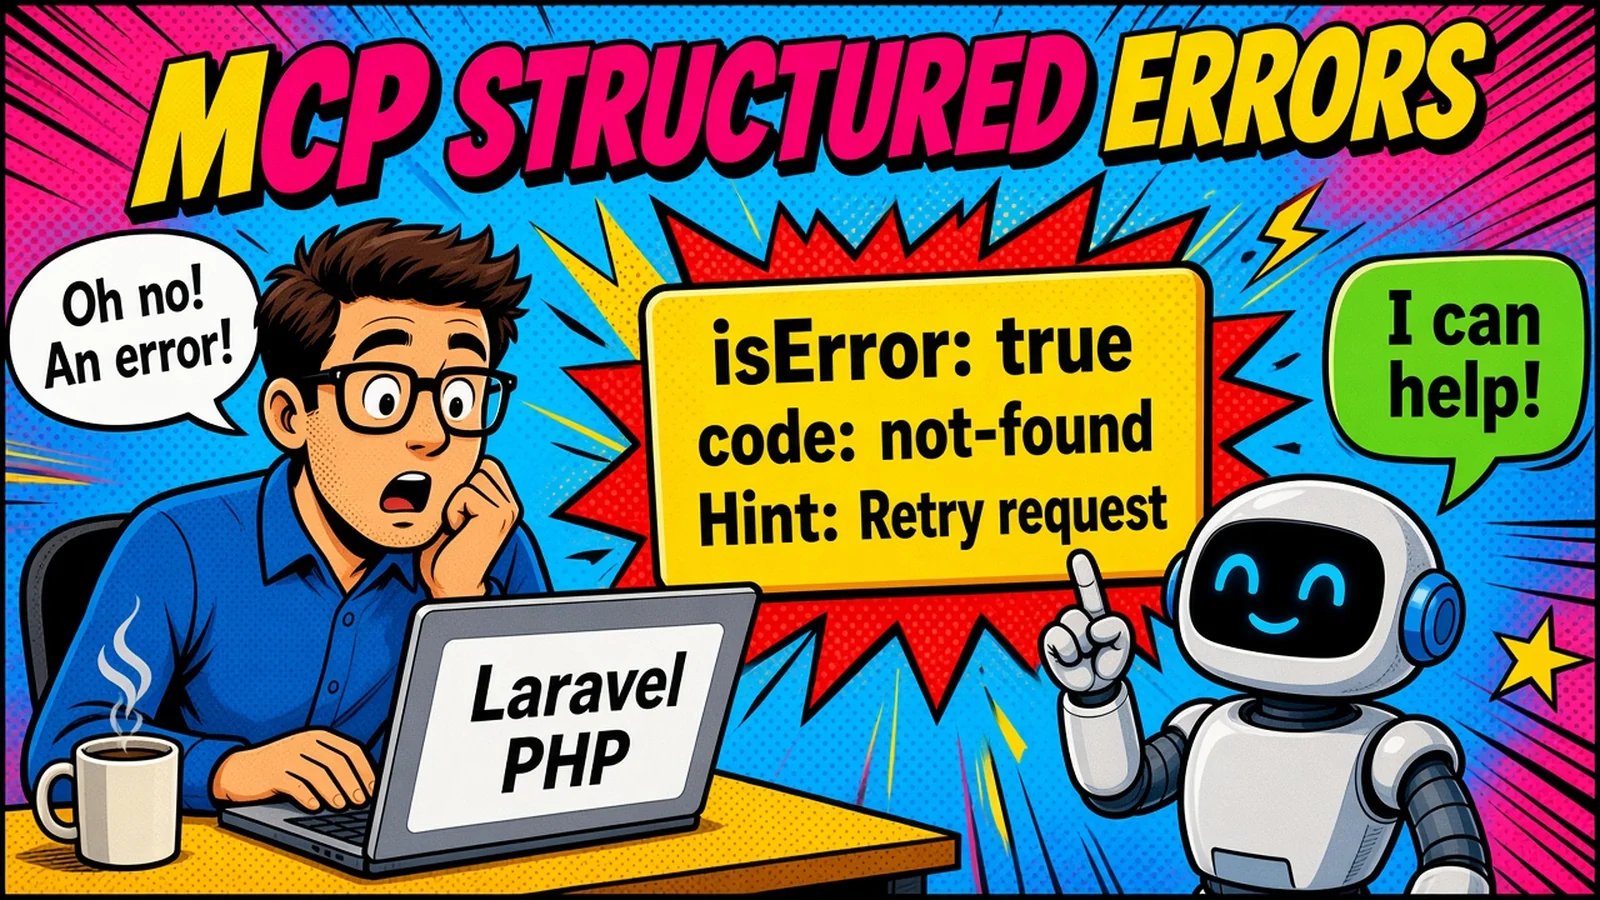
MCP tool errors agents can actually recover from
Throwing exceptions hides failures from the model. MCP wants isError tool results with actionable text, mapped from Laravel domain failures and audited like auth denials.
Read post →
-
 Laravel
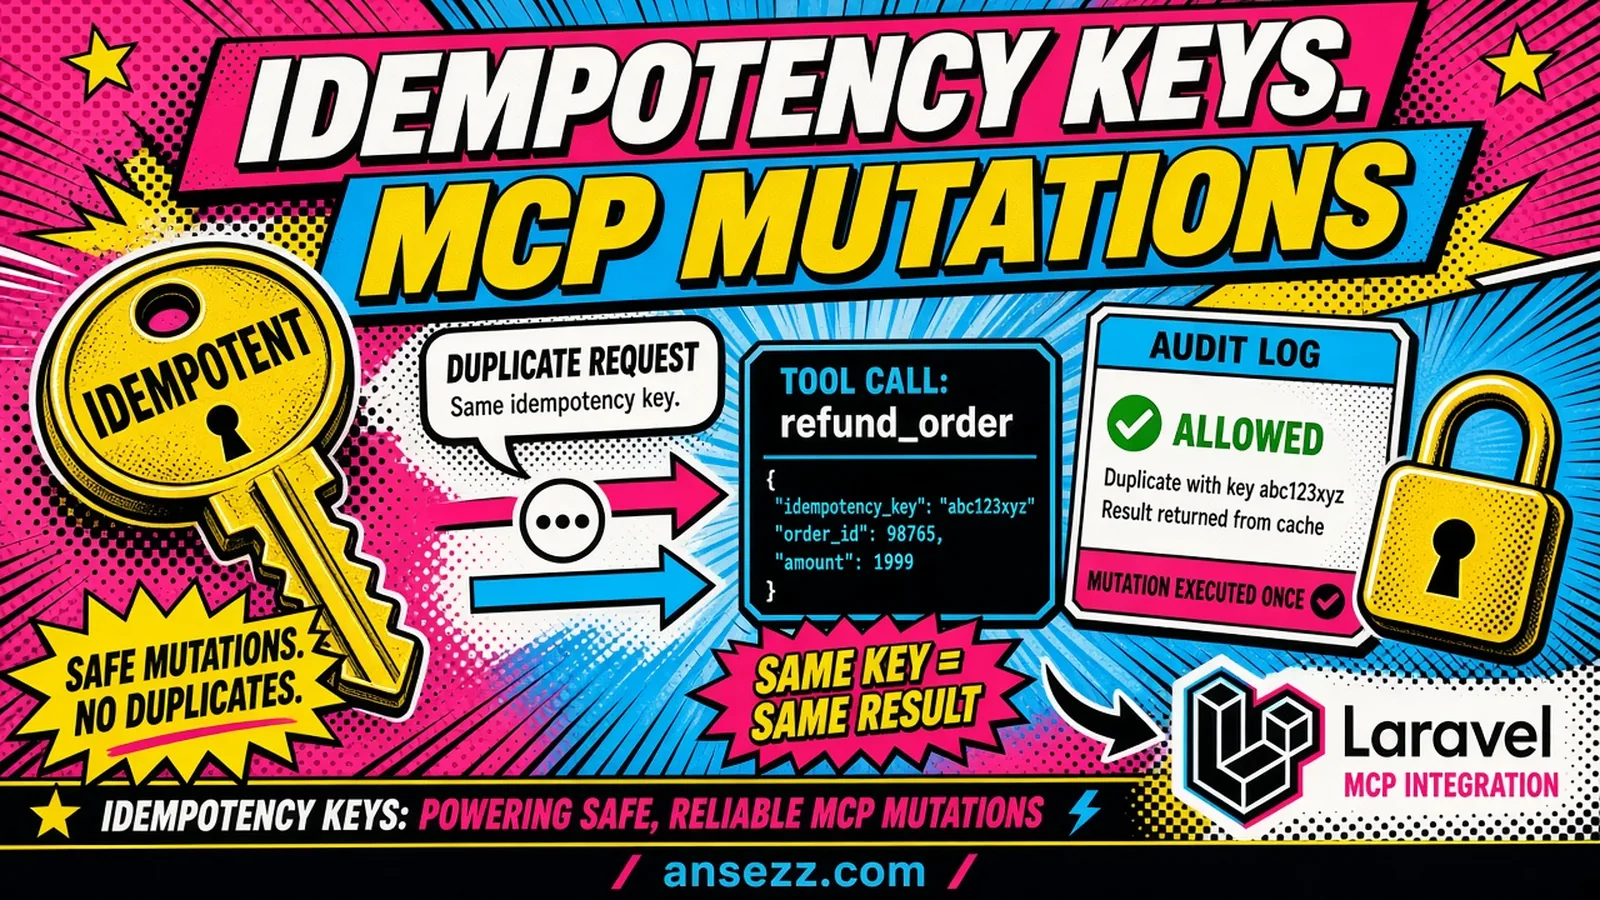
Idempotency keys for MCP mutations in Laravel
Refunds, seat resets, and password emails need more than audit logging. Client-supplied idempotency keys, server-side short-circuits, and race-safe storage under Octane.
Read post →
-
 Laravel
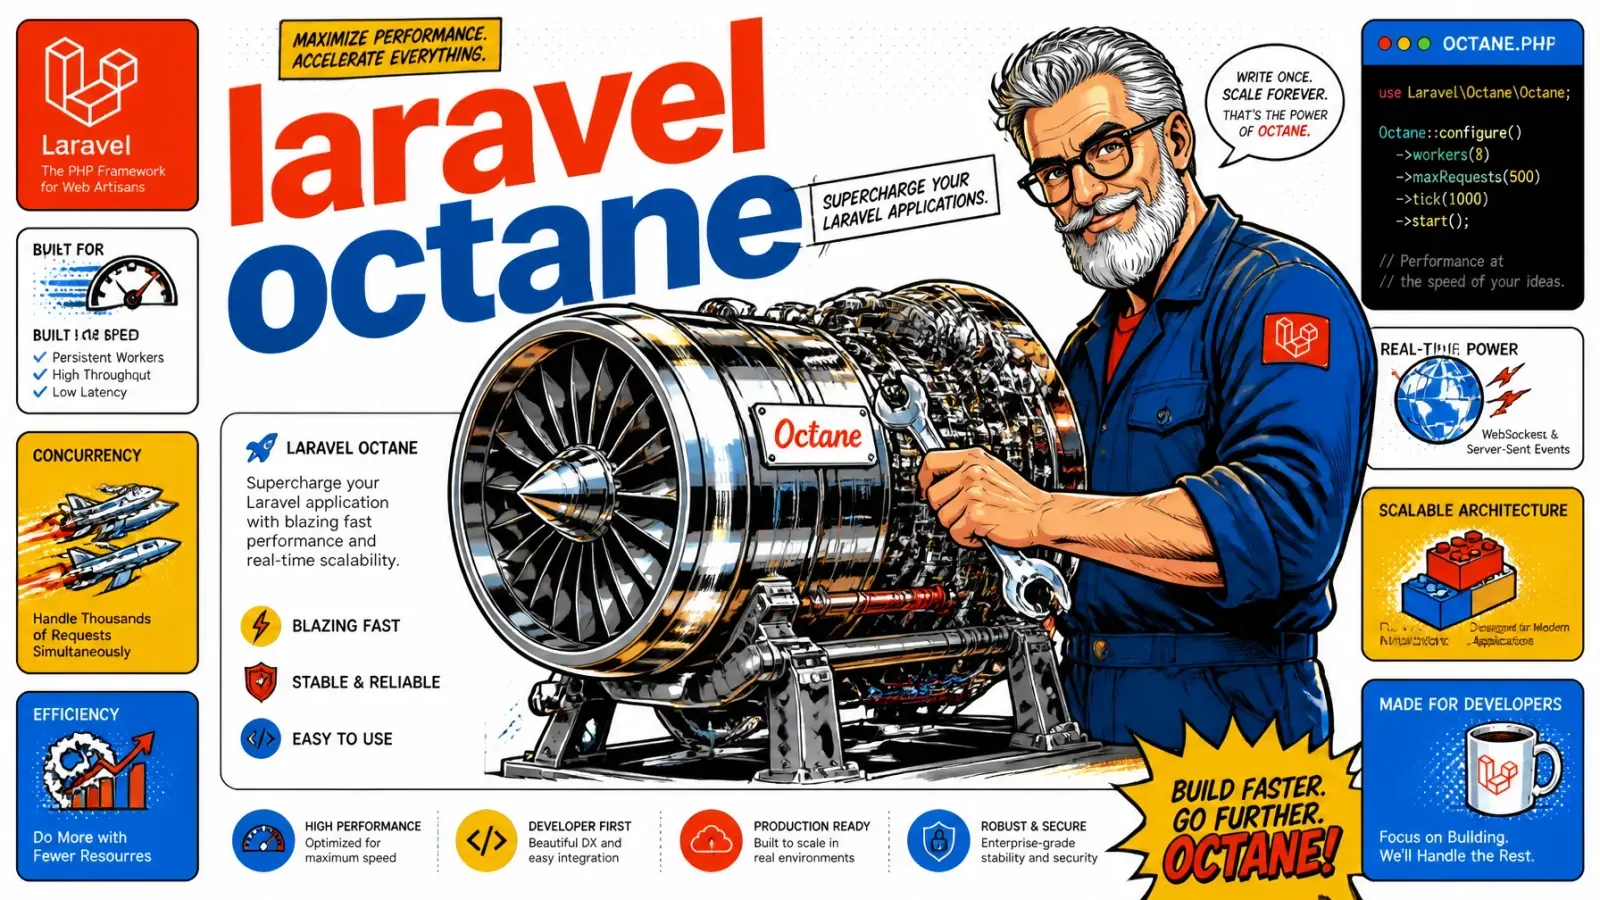
 Octane for high-traffic PHP apps
Laravel Octane boots your app once and keeps it warm in memory, feeding requests through a worker pool. How to cut boot overhead and scale to high traffic.
Read post →
-
 Laravel
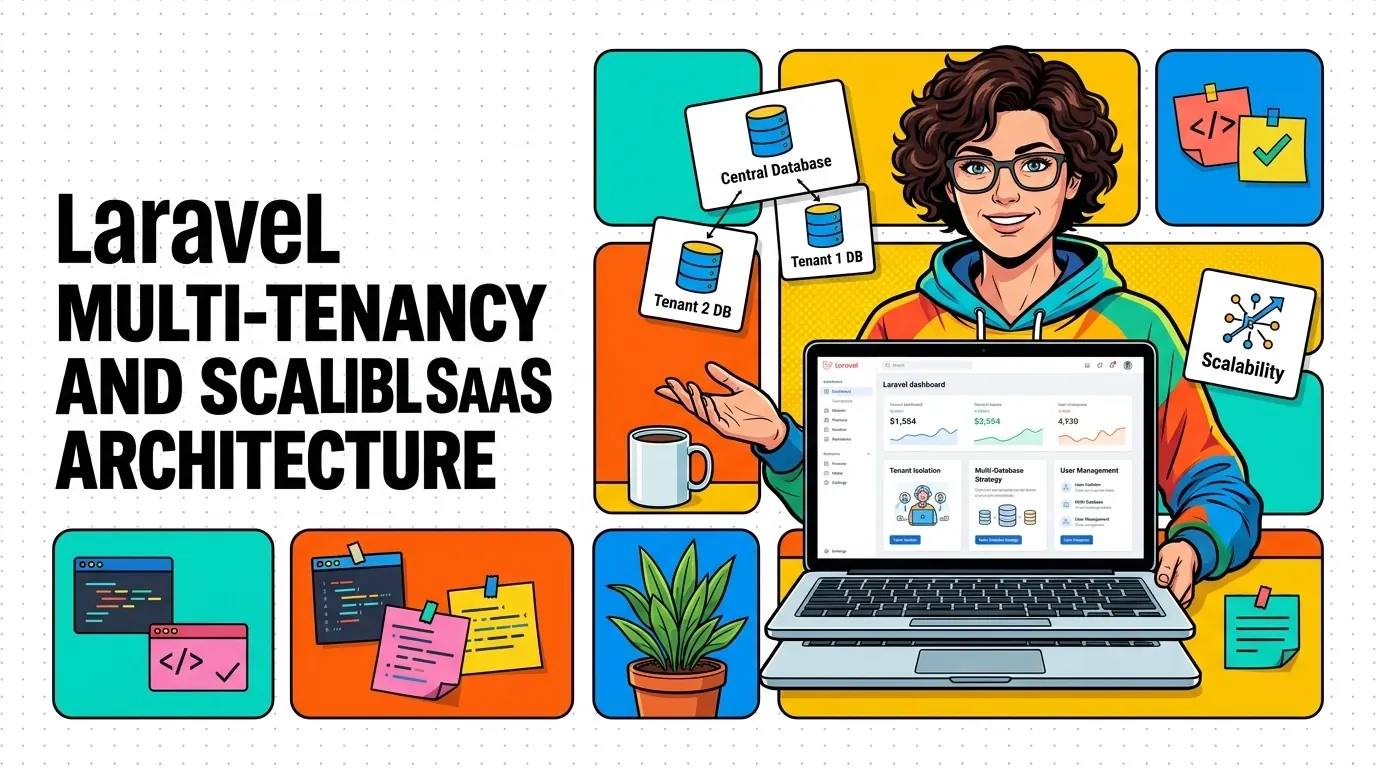
 multi-tenancy: a scalable SaaS architecture
Single DB vs multi-DB, global scopes that stop data leaks, stancl/tenancy in production, isolated storage, automated migrations, and a Docker plus Cloud setup.
Read post →