▸ Tag · #security
Security.
Security for systems that talk to models and to money: authentication, webhook verification, and denial-of-wallet on metered AI endpoints.
-
 Laravel
MCP auth and audit logging in a Laravel SaaS
An MCP server on Laravel is only as safe as its tenancy boundary. Scoped tool auth, request-bound actor context, and an audit log you can actually read at 3am.
Read post →
-
 Shopify
Building secure agentic commerce on Shopify in 2026
How agentic commerce on Shopify stays safe: UCP negotiation, an MCP governance layer, scoped credentials, signed requests, and human approval at checkout.
Read post →
-
 AI
Grok Bot vs OpenAI dots: a team of bots or one agent
OpenAI dots and Grok Bot both give an AI agent its own cloud computer. Here is how they differ on teams, control, routines and access, and which fits your work.
Read post →
-
 AI
Run your business with one AI assistant per area
A simple setup for running any business with AI assistants: one hub, one bot per area of work, strict scopes, drafts before sends, and routines that stay quiet.
Read post →
-
 Architecture
HITL gates for agent mutations
Human-in-the-loop risk gates for refunds, inventory, and spend. Verify mutations after tool calls so agents cannot declare early victory.
Read post →
-
 Laravel
MCP OAuth PKCE for multi-tenant SaaS
Laravel MCP requires PKCE S256 and prefers Client ID Metadata Documents. How multi-tenant SaaS should bind workspace at consent and avoid common agent auth failures.
Read post →
-
 Shopify
Buyer-linked tokens for agent checkout
Exchange a Shop session for a Shopify buyer-linked JWT (~60 minutes, no refresh) so signed-in agents can personalize catalog and complete checkout.
Read post →
-
 Shopify
UCP agent profiles are the new OAuth app
Host a UCP agent profile URL, declare cart and checkout capabilities, and climb Anonymous, Signed, and Token trust tiers for Shopify MCP.
Read post →
-
 Laravel
MCP tool errors agents can actually recover from
Throwing exceptions hides failures from the model. MCP wants isError tool results with actionable text, mapped from Laravel domain failures and audited like auth denials.
Read post →
-
 Laravel
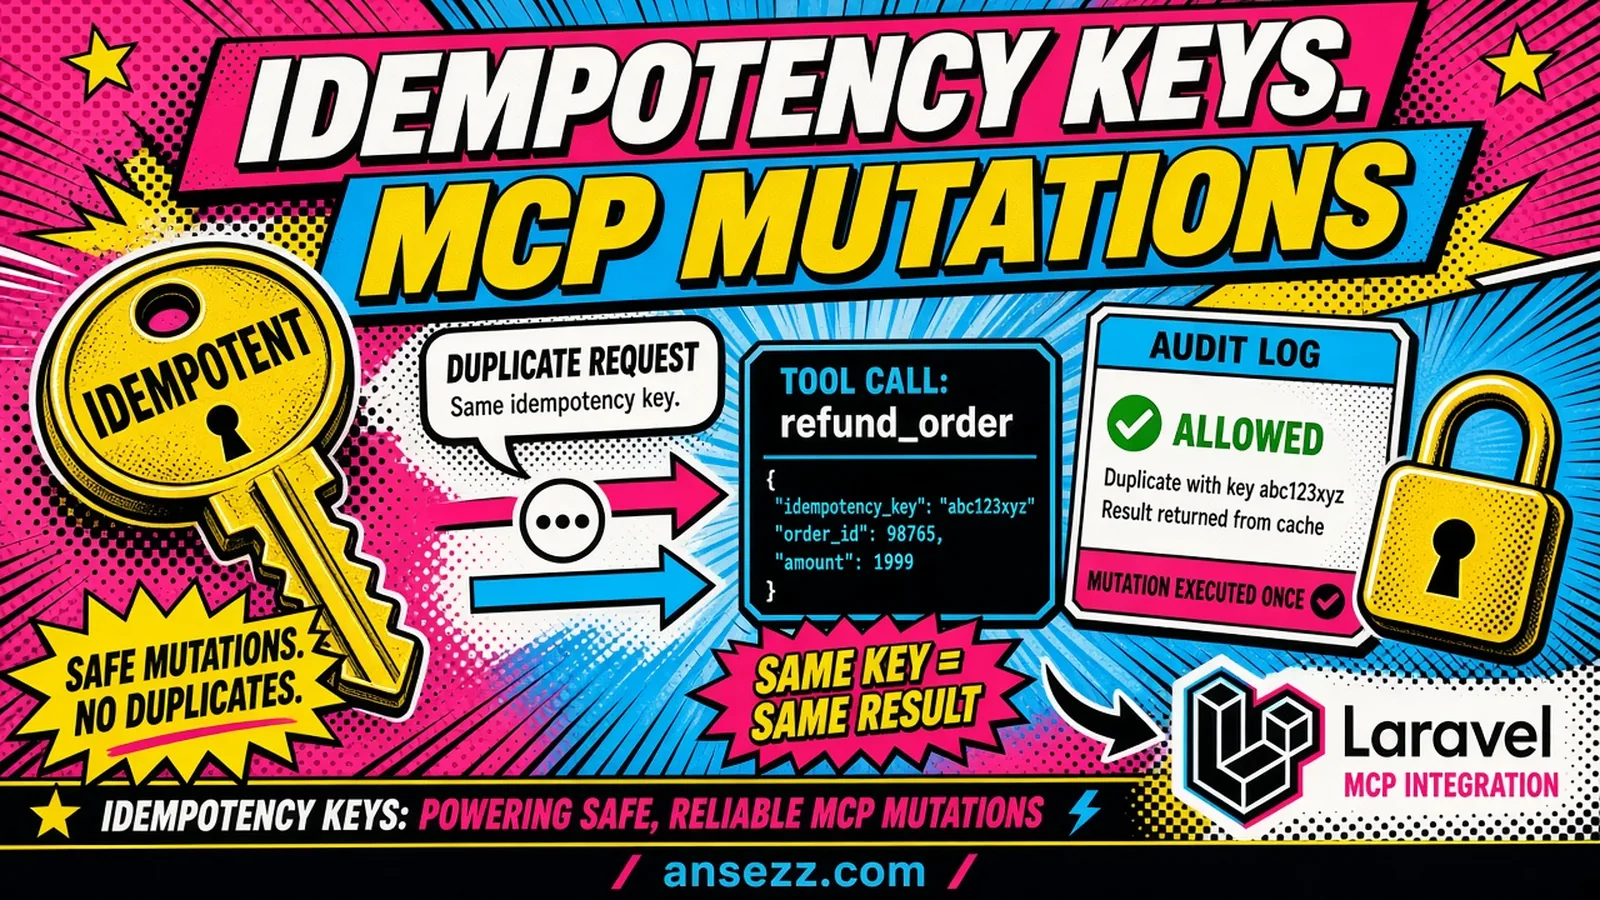
Idempotency keys for MCP mutations in Laravel
Refunds, seat resets, and password emails need more than audit logging. Client-supplied idempotency keys, server-side short-circuits, and race-safe storage under Octane.
Read post →
-
 DevOps
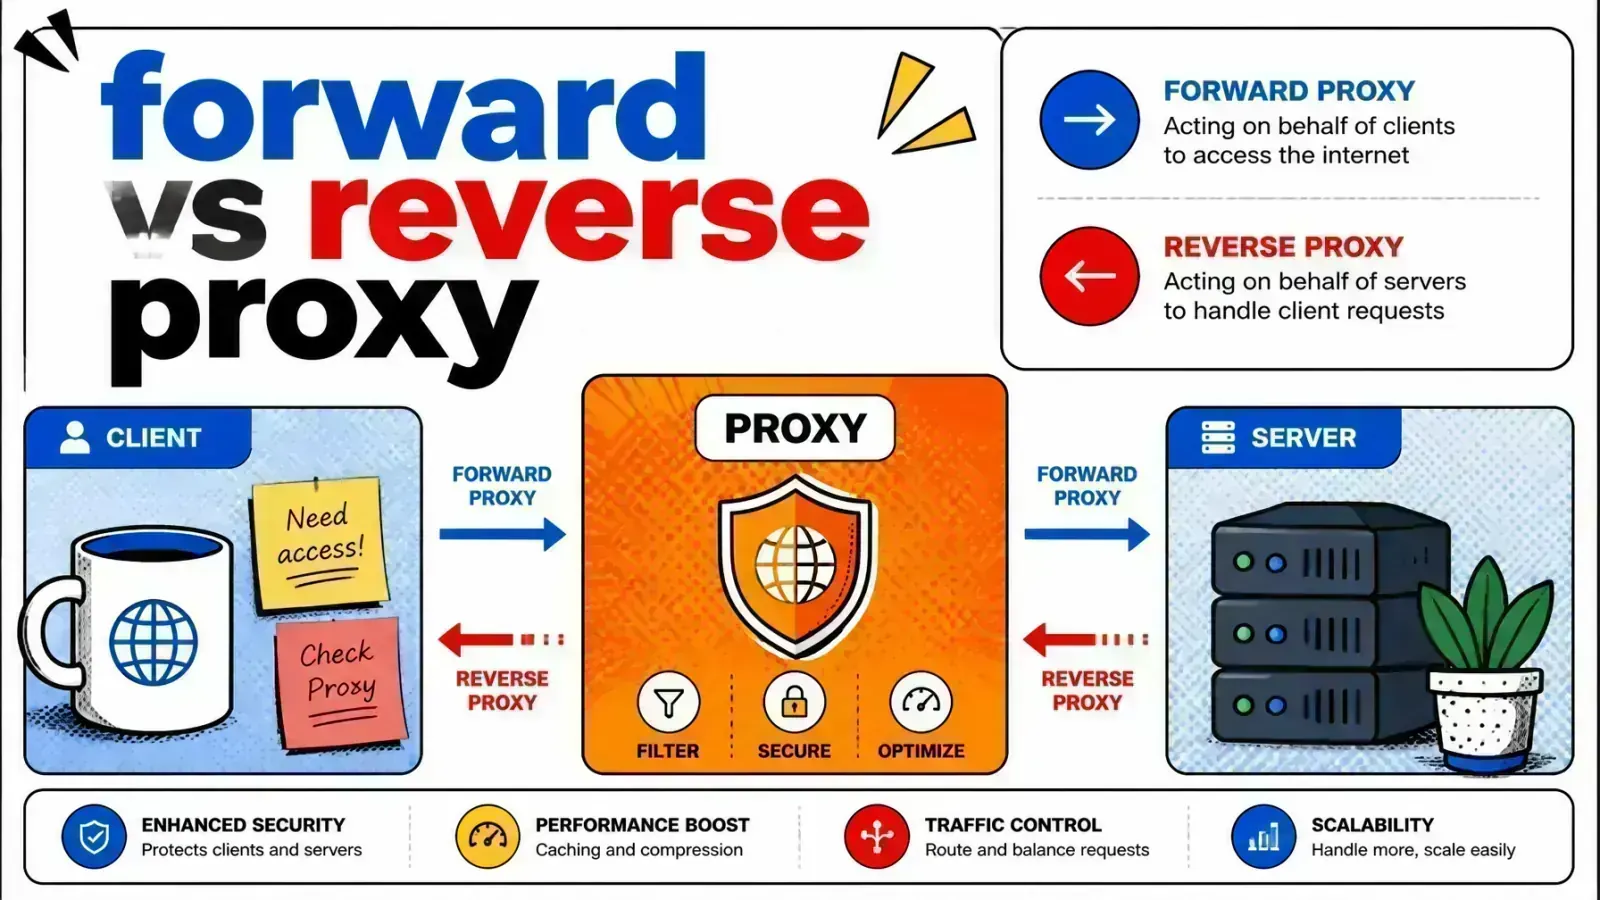
Forward proxy vs reverse proxy: the technical guide
A forward proxy hides the client; a reverse proxy hides the server. How traffic direction shapes your load balancing, SSL termination, and security design.
Read post →
-
 Architecture
Rate limiting: protecting your AI wallet
One runaway agent loop can mean a $5,000 LLM bill. Why request-per-second limits lie, and how hierarchical token-bucket limits protect your margins.
Read post →
-
 Architecture
API gateway: the front door of your AI stack
Stop exposing LLM providers to your frontend. The API gateway pattern for AI apps: tenant isolation, model aliases, rate limiting, and streaming-safe timeouts.
Read post →